AI Adoption Is Already Decentralized
Employees do not always wait for formal enterprise AI programs.
They may already be using:
- ChatGPT
- Claude
- Gemini
- AI browser extensions
- AI writing tools
- coding assistants
- meeting transcription tools
- AI design platforms
- third-party copilots
This leads to the proliferation of Shadow AI. The organization may not know which tools are being used, what data is being submitted, or how those vendors handle the information.
That is Shadow AI.
Why Shadow AI Is Different From Traditional Shadow IT
Traditional Shadow IT usually meant an unsanctioned SaaS application.
Shadow AI adds additional dimensions:
- user prompts may contain sensitive data
- files can be uploaded
- source code may be exposed
- responses can influence business decisions
- AI tools may retain data
- browser extensions may access page content
- agents may interact with internal applications
- APIs may use embedded credentials
The risk is not only where the application runs.
It is what information it can see and what actions it can influence.
Risk 1: Sensitive Data Leakage
Employees may inadvertently paste:
- customer records
- contracts
- PHI
- financial data
- internal strategy
- intellectual property
- credentials
- source code
into external AI platforms.
The organization may then lose visibility into where that data resides.
Risk 2: Unapproved Vendors
Security teams may not have reviewed:
- retention
- model training practices
- administrative access
- breach notification
- geographic processing
- encryption
- subcontractors
- data deletion
That creates third-party risk.
Risk 3: Identity and Access
AI applications increasingly integrate with enterprise systems.
An AI tool may request access to:
- Google Workspace
- Microsoft 365
- Slack
- GitHub
- Salesforce
- cloud storage
- CRM
- internal APIs
Once connected, the AI application may gain access far beyond a simple browser prompt.
Risk 4: Browser Extensions
AI browser extensions are particularly important.
Some may have permissions to:
- read page content
- modify pages
- access tabs
- interact with websites
- capture user input
That means an AI extension could potentially see sensitive business information being displayed in the browser.
Risk 5: Regulatory Exposure
For regulated industries, Shadow AI can create more than a cybersecurity concern. It can also introduce compliance, audit, privacy, and contractual risk.
The challenge is that employees may begin using AI tools before security, legal, compliance, or procurement teams have reviewed how those tools handle data.
That can create questions around:
- where sensitive information is processed
- whether data is retained by the AI provider
- whether prompts or uploaded files are used for model training
- who can access the information
- whether the service has appropriate security controls
- whether the organization has approved the vendor
- whether logs exist to show how the tool was used
- whether the use of the AI service is covered by existing policies and risk assessments
Healthcare organizations may have concerns around PHI and HIPAA requirements.
Financial organizations may face obligations around data governance, privacy, recordkeeping, and third-party risk.
Legal firms may risk exposing client-confidential or privileged information.
Organizations pursuing or maintaining SOC 2 Type II compliance can face a similar problem.
A SOC 2 Type II examination is intended to evaluate whether relevant controls are not only designed appropriately, but also operating effectively over a defined period of time. Shadow AI can undermine that control environment when employees use unapproved AI tools outside established security and vendor-management processes.
For example, imagine an organization has SOC 2 controls requiring:
- approved third-party vendors to undergo security review
- sensitive customer information to be handled only in authorized systems
- access to production or confidential information to be logged and monitored
- security policies to be communicated and enforced
An employee then uploads customer information into an unapproved generative AI platform to summarize a report.
Even if no breach occurs, the organization may now have difficulty demonstrating that its documented control environment was consistently followed.
An auditor may reasonably ask:
Was the AI provider evaluated as a third party?
Was the data authorized to leave the approved environment?
Can the organization show who used the tool and what information was submitted?
Were retention, access, and security requirements evaluated?
Was the activity detected or governed by existing controls?
That is why Shadow AI can become an auditability problem, not just a technology problem.
The underlying issue is the same across regulated and compliance-driven environments:
The business may not know where sensitive data is being sent, who has access to it, or whether its existing security controls still apply once that data enters an unapproved AI service.
A practical AI governance program should therefore connect Shadow AI discovery with data classification, vendor risk management, access control, logging, policy enforcement, and compliance monitoring.
The business may not know where sensitive data is being sent.
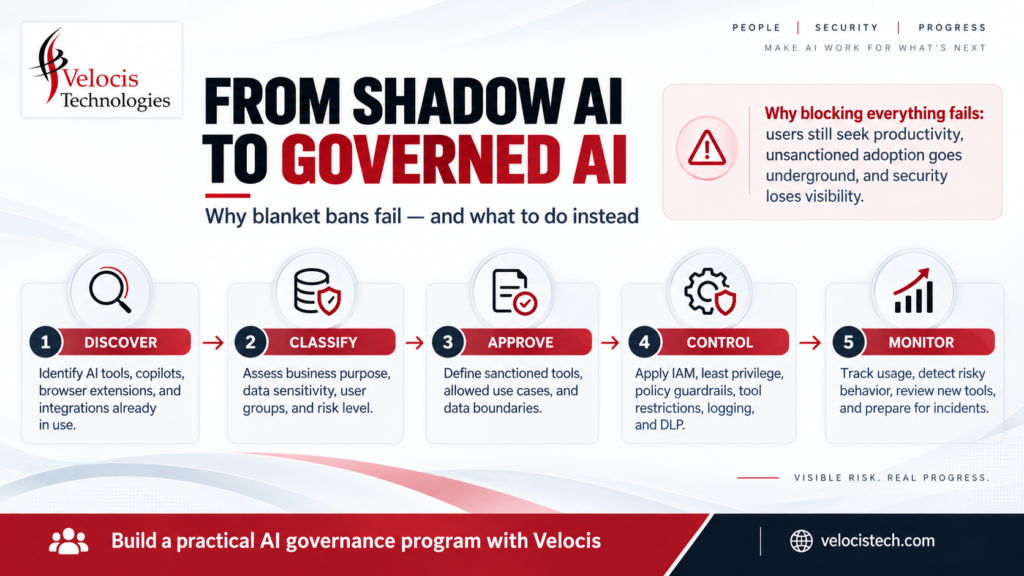
Blocking Everything Usually Fails
A blanket AI ban may look simple.
But employees often adopt tools because they solve real business problems.
If security only says “no,” users may simply move further outside approved channels.
A better approach is:
Discover → Classify → Approve → Control → Monitor
NIST AI RMF Resources and Playbook
What Organizations Should Do
Start with:
1. Discover AI usage
Identify which AI services are being accessed.
2. Classify use cases
Understand what employees are actually doing.
3. Define approved tools
Give users safe alternatives.
4. Establish data boundaries
Define what information may be submitted.
5. Apply identity controls
Limit integration permissions.
6. Monitor usage
Look for emerging risk.
7. Train users around real scenarios
Avoid generic “AI is risky” training.
Use concrete examples.
The Goal Is Visibility, Not Prohibition
The strongest AI security program is not the one that blocks the most tools.
It is the one that knows:
What AI is being used.
Who is using it.
What data it can access.
What actions it can perform.
That is how organizations move from Shadow AI to governed AI.
CTA
Do you know where AI is already operating inside your organization?
Request a Velocis AI Usage & Exposure Assessment.