Velocis Technologies brings together cybersecurity professionals with experience across security operations, enterprise and cloud security, vulnerability management, incident response, strategic partnerships, and business leadership. The company is built around a simple idea: security has to work in the real environment, not only on paper.
Our team supports organizations in the United States and globally with practical cybersecurity services designed to strengthen visibility, reduce risk, improve response, and help security programs adapt as threats and technology change. From 24/7 security operations to digital forensics, AI security, risk assessment, and emerging technology, Velocis combines technical expertise with an operational focus.
Cybersecurity Expertise Built Around Real Operations
Effective cybersecurity depends on more than technology. It requires people who understand how security controls affect business operations, how incidents unfold under pressure, how risk should be prioritized, and how security programs need to evolve over time.
Velocis combines strategic and technical leadership across several disciplines. Security operations teams monitor and investigate threats. Cybersecurity architects and analysts help organizations strengthen controls and reduce exposure. Business and partnership leadership helps connect those capabilities with the technologies, service providers, and customer environments they need to support.
Meet the Velocis Leadership Team
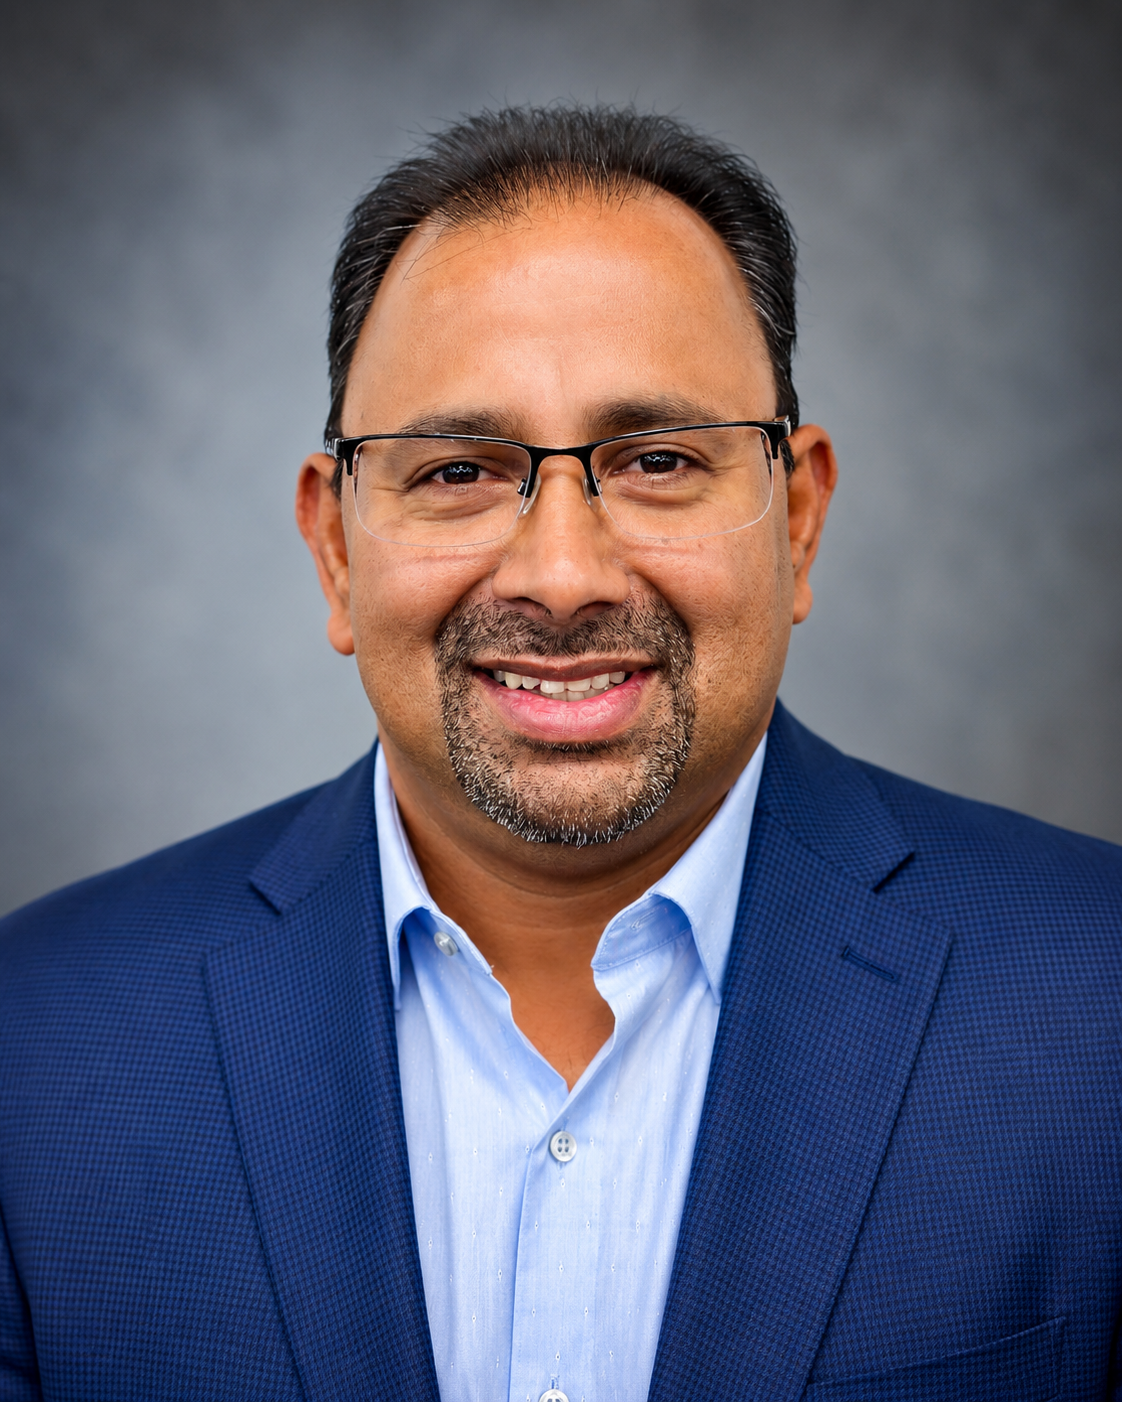
Soy Joseph
Soy brings more than 25 years of hands-on experience architecting, developing, implementing, and managing technical solutions. His cybersecurity expertise spans enterprise security, cloud security, risk assessment, security operations, and remediation strategy.
At Velocis, he oversees cybersecurity initiatives and leads analysts supporting continuous threat hunting and monitoring. His work also extends into emerging technologies including quantum computing, AI/ML, and generative AI.
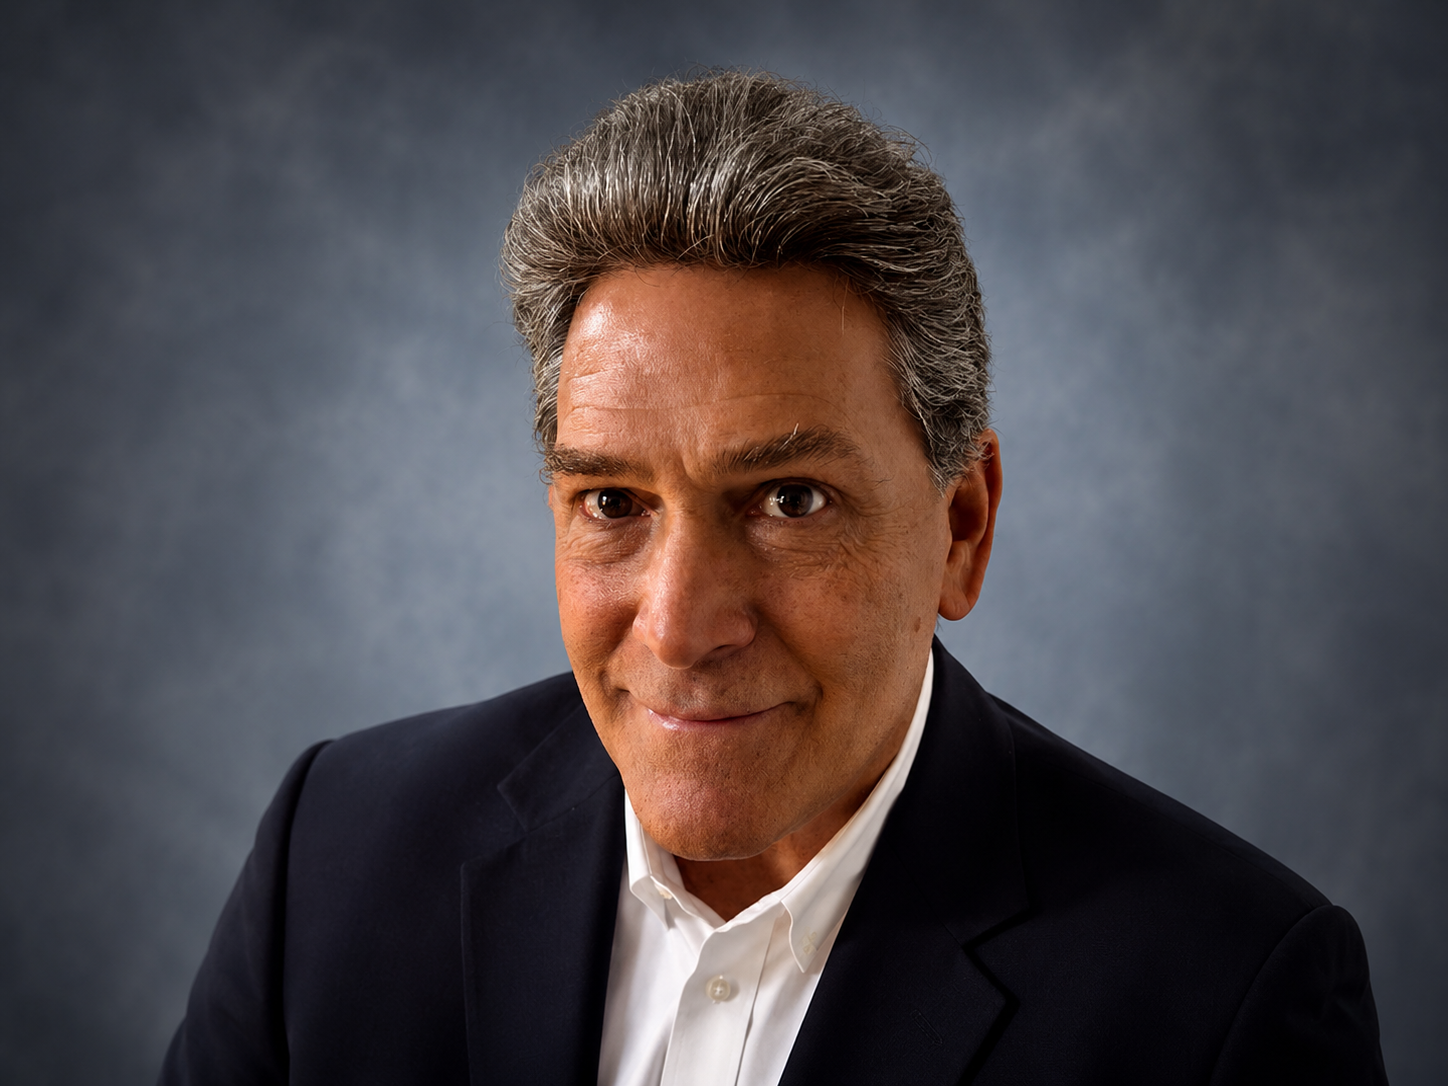
Dan Smith
Dan brings more than 40 years of sales and business-development experience across products, services, and multiple industries, with a record of building revenue and long-term customer relationships.
His experience includes direct and channel sales through GSIs, MSSPs, consultancies, and professional-services organizations, helping connect Velocis capabilities with customers and strategic partners.
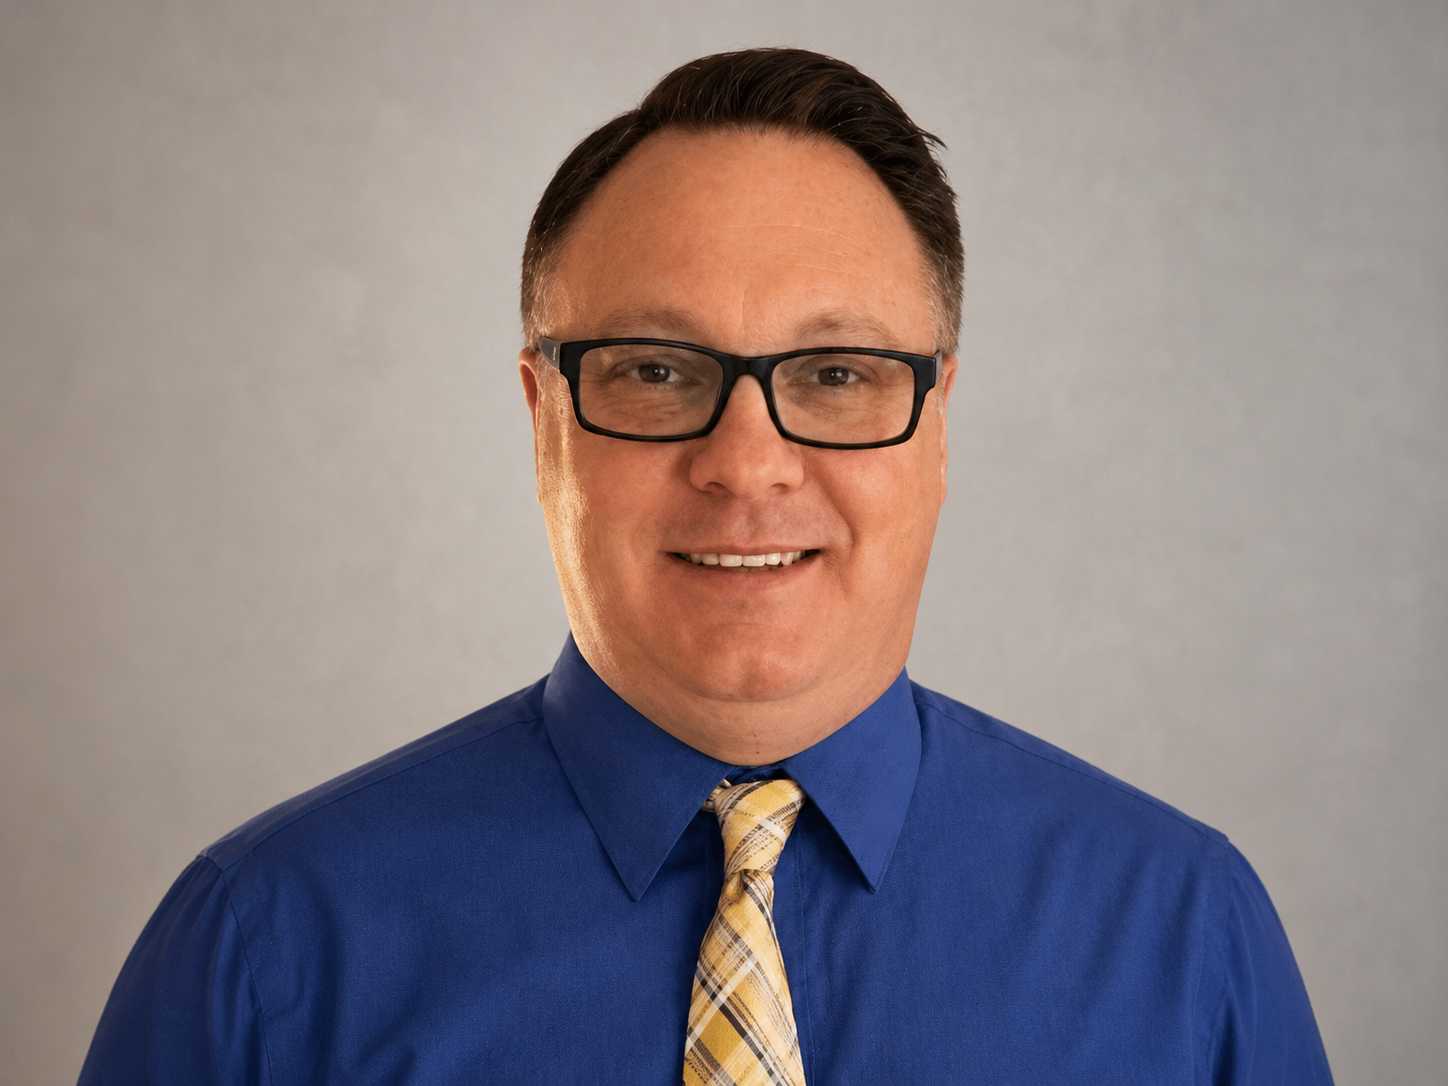
Shawn Spence
Shawn is an information-security leader and architect with more than 30 years of experience across security domains and industries. His work focuses on aligning security initiatives with business goals while maintaining strong technical and operational execution.
At Velocis, he oversees project implementation and leads a global team of security analysts and engineers with a focus on customer service, continuous education, and technical capability.
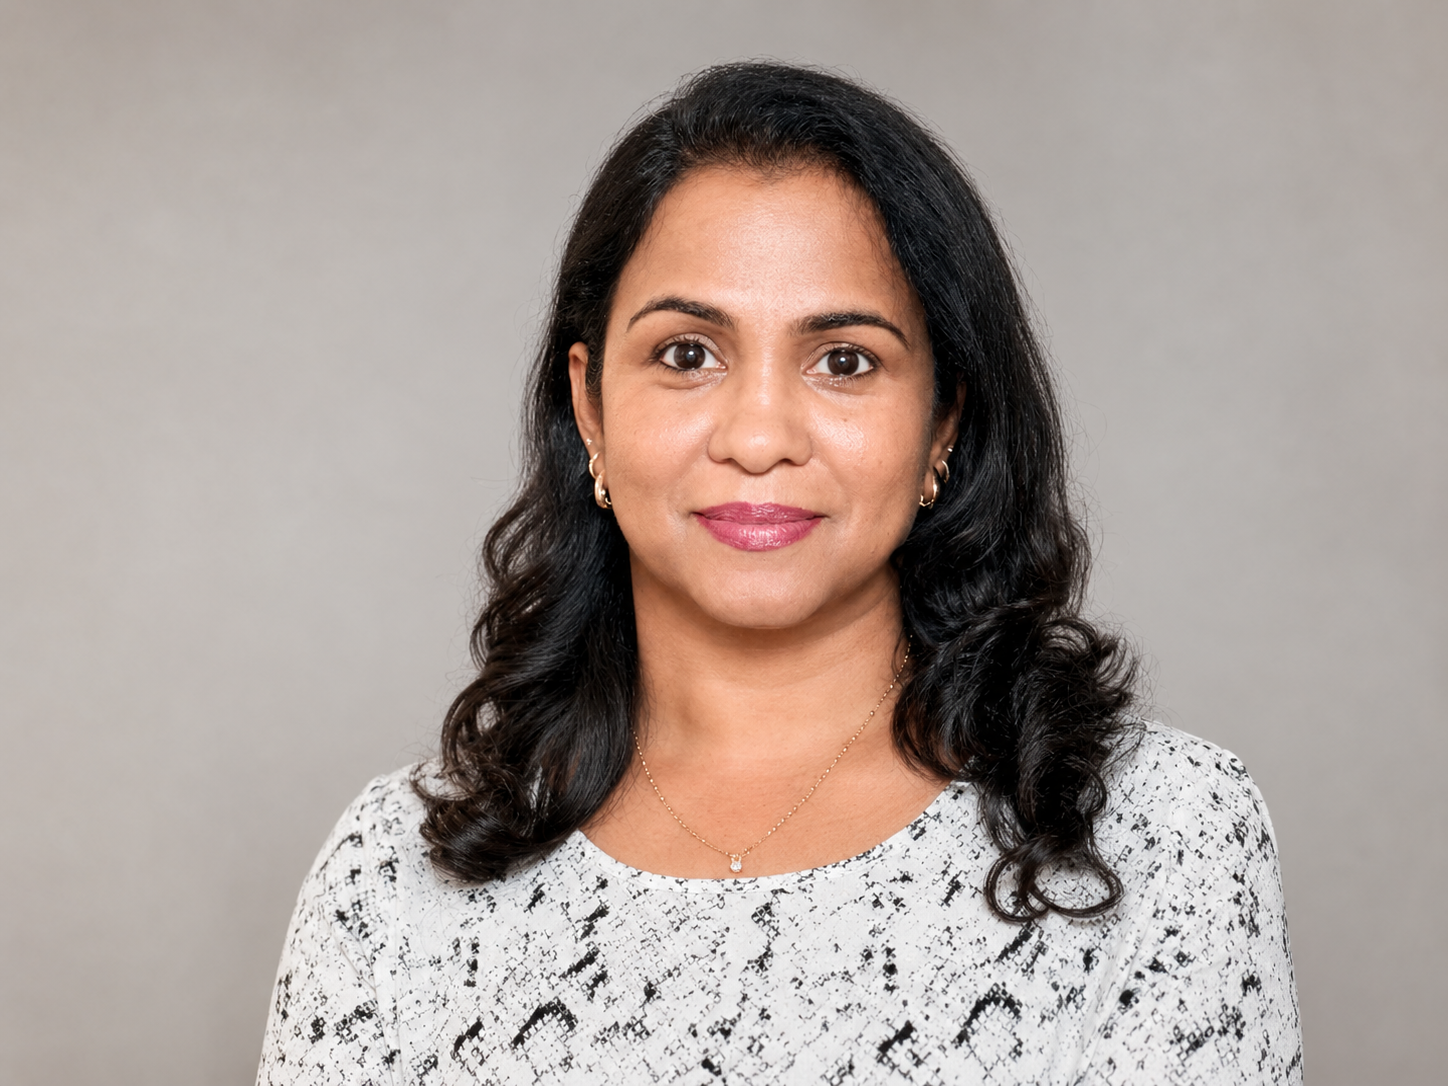
Liji George
Liji brings more than 15 years of experience managing financial operations in the software industry, with expertise in financial planning, analysis, risk management, and sustainable growth.
Her role supports strategic decision-making across the business and helps align financial planning with the broader goals of Velocis Technologies.
Advisory Board
Velocis Technologies works with experienced advisors who bring perspectives from research, industry, government, academia, emerging technology, and strategic innovation.
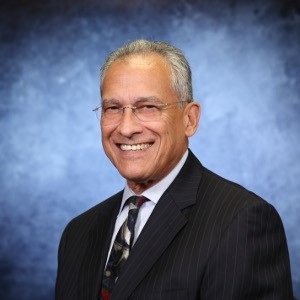
Victor A. Fishman, Ph.D.
Dr. Victor A. Fishman is Executive Director of the Texas Research Alliance and brings extensive experience across industry, government, academia, applied research, technology commercialization, and cross-sector innovation.
As a member of the Velocis Technologies Advisory Board, Dr. Fishman provides strategic guidance supporting the development and evolution of Q-SOC™ — Velocis’ quantum-ready security operations platform. His advisory focus includes emerging technology strategy, applied research, innovation ecosystems, commercialization, and collaboration across industry, academia, and the public sector.
His perspective supports Velocis as we advance Q-SOC™ capabilities in areas including quantum security readiness, post-quantum cybersecurity, crypto-agility, identity-centric security operations, AI-enabled security, and the transition from traditional SOC architectures toward future-ready security operations.
Dr. Fishman also advises on opportunities to connect Q-SOC™ with research institutions, technology partners, industry leaders, and innovation communities that can help accelerate validation, collaboration, and commercialization.
What Clients Say About Working With Velocis
A long-term information-security client describes Velocis as a proactive partner that helps identify risk, prioritize mitigation, and turn assessments into practical improvements to the organization’s security posture.
A client in the trading industry credits Velocis with uncovering previously unknown vulnerabilities through risk assessment and testing, then helping the organization prioritize resources and close critical security gaps.
A technical director describes Velocis’ incident-response team as moving quickly during a ransomware event, containing the infection and helping prevent lateral movement across the network during recovery.
Security That Connects People, Process, and Technology
Velocis works across managed security operations, cyber defense, investigations, risk, identity, cloud, and emerging technology. The strength of that model is the connection between disciplines: security operations can surface issues that require deeper forensic investigation; risk assessments can reveal gaps that need continuous monitoring; identity and cloud controls can reduce the exposure behind recurring incidents.
Organizations looking to strengthen day-to-day detection and response can explore Cyber Defense. Teams dealing with an active incident or requiring evidence-driven investigation can engage our Digital Forensics and Incident Response capability. For a broader view of security posture and control gaps, start with a Security Risk Assessment.
Be a Cyber Defender.
Velocis is interested in people who want to solve real cybersecurity problems, keep learning, and help organizations operate more securely.